
SBI has ordered an independent cybersecurity investigation after examining nearly 3.75 lakh records, while questions remain over the source of the exposure and risks to customers.
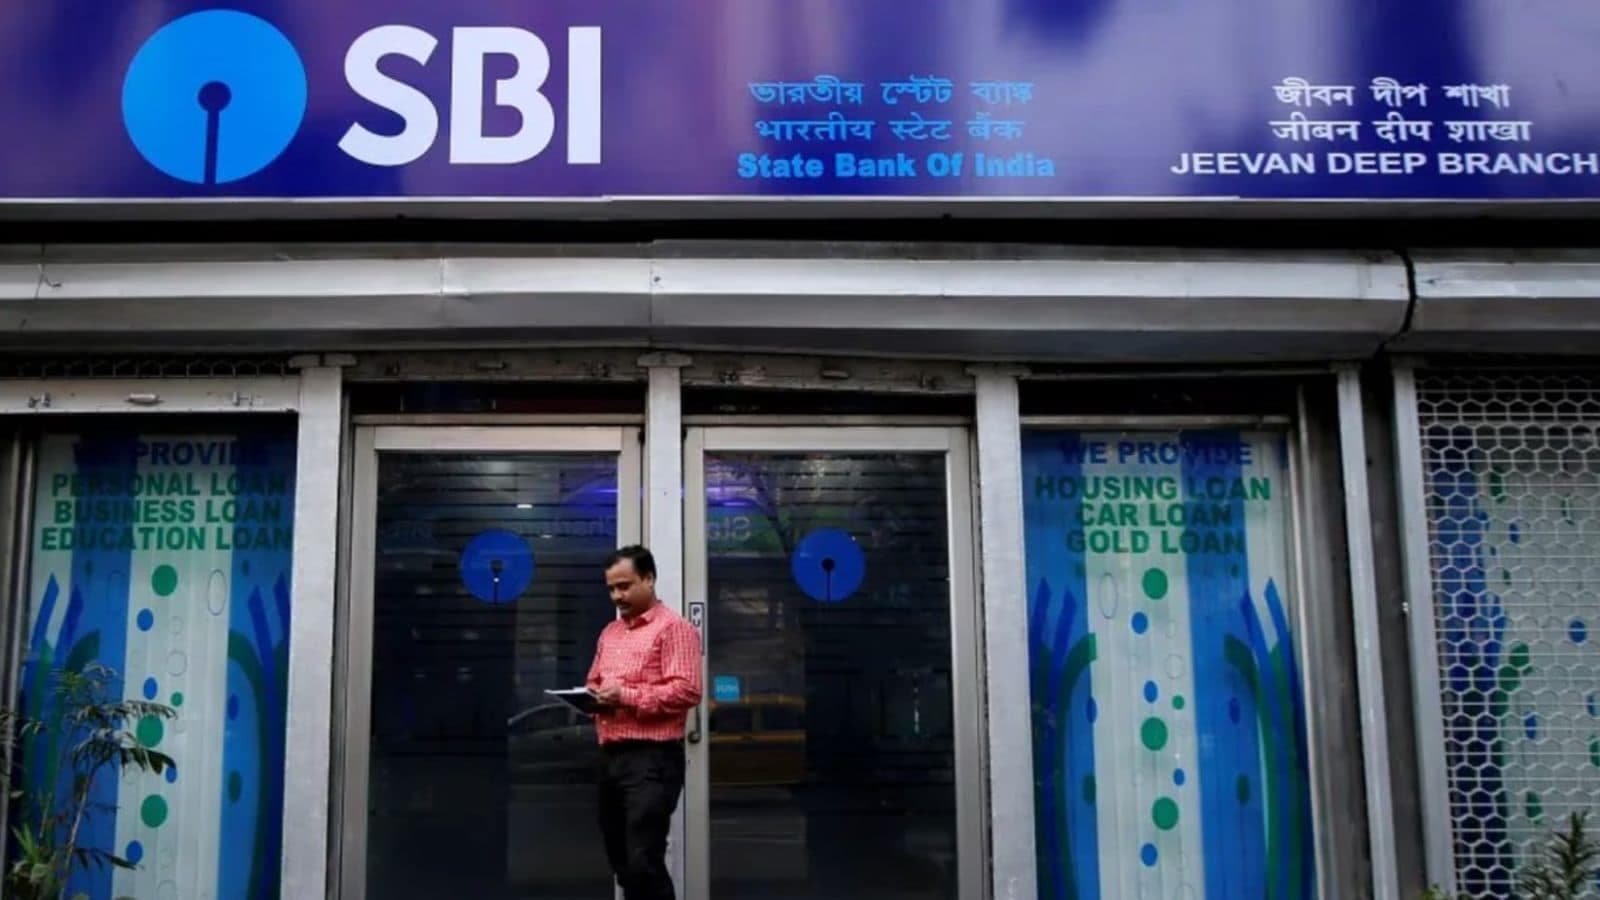
The State Bank of India (SBI) has disclosed a suspected customer data breach after its preliminary investigation identified 3,897 records containing personal information on the dark web, raising concerns over the security of sensitive banking data and its potential misuse.
The country's largest public sector lender informed stock exchanges on Wednesday that the records were identified during an initial examination of approximately 3.75 lakh entries available on the dark web. The bank has yet to determine how the information was exposed, whether the complete dataset is authentic or how many customers may ultimately be affected.
According to the bank's regulatory disclosure, the information identified includes customer names, registered mobile numbers, dates of birth, gender, email addresses and residential addresses. Branch information, Customer Information File (CIF) identifiers, lead identification numbers and metadata associated with loan applications and related records were also among the details reported.
SBI said it received alerts on October 16 from its threat intelligence service provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team (CERT-In), the national agency responsible for responding to cybersecurity incidents.
Following the alerts, the bank activated its incident response procedures and appointed an independent cybersecurity agency empanelled with CERT-In to investigate the suspected compromise.
"The Bank promptly activated its cyber incident response and containment protocols," SBI said in its disclosure.
The investigation will seek to establish whether the exposed records are genuine and complete, identify their possible source and determine the extent of the security incident. Investigators will also assess the potential consequences for customers whose personal information may have been compromised.
"A detailed assessment is currently underway, and appropriate remedial and preventive measures are being implemented as required," the bank said.
SBI maintained that the incident had not materially affected its core banking operations, financial performance or business continuity. Its banking services continue to function normally, according to the disclosure.
However, the bank's statement does not establish whether the exposure originated from its own infrastructure, a third-party service provider or another source. It also does not clarify whether the customers whose records were identified have been individually informed.
Hacker group claimed access to 3.75 lakh records
The bank's disclosure follows reports of an alleged breach by a group identifying itself as Siriusim, which claimed to have obtained a large collection of information associated with SBI customers.
The claims, circulated through the cybersecurity monitoring account CyberPulse56 on social media platform X, referred to approximately 3.75 lakh entries in CSV format and 2,722 PDF documents.
The purported documents included loan applications, account-opening forms, residential information and other supporting records associated with banking applications.
The claims circulated before SBI formally acknowledged the suspected data exposure. However, the authenticity of the documents, their origin and the group's claimed access have not been independently established.
SBI's identification of 3,897 records containing personally identifiable information does not mean that the remaining entries have been verified as genuine customer records or that an equivalent number of individual customers were affected.
The distinction is important because the total number of files or entries in a dataset cannot, by itself, establish the number of people affected by a cybersecurity incident.
Previous incidents raised concerns over banking data security
The latest disclosure comes months after another public sector lender, Bank of Baroda, reported a cybersecurity incident involving unauthorised access to information through a compromised employee email account.
In July 2026, a hacker claimed to have released a substantial collection of Bank of Baroda data, reportedly including customer records and internal banking documents.
Bank of Baroda subsequently acknowledged that an employee's email account had been compromised, resulting in unauthorised access to certain information. It maintained that its core banking systems had not been accessed and remained secure. The bank initiated a forensic investigation to establish the extent of the incident.
SBI itself faced questions over customer information security in January 2019 after technology publication TechCrunch reported that an improperly secured server associated with its SBI Quick service could have exposed customers' account balances and transaction-related information.
The bank subsequently said its investigation had identified a configuration problem involving the process used by telecom providers and aggregators. SBI maintained that its servers were secure and that no breach had occurred within its systems.
An earlier banking security scare in October 2016 prompted several Indian banks to replace debit cards or advise customers to change security credentials after a potential compromise affecting up to 3.25 million debit cards.
SBI said at the time that approximately 620,000 of its cards were considered vulnerable and were being replaced as a precaution. The bank attributed the potential risk to a breach outside its network.
Although these incidents involved different systems and circumstances, they illustrate how risks to customer information can arise through multiple points in the banking ecosystem, including external infrastructure and service providers.
What the suspected exposure means for SBI customers
The disclosure of personal information does not necessarily mean that customers' bank accounts have been accessed or money has been withdrawn.
However, information such as names, dates of birth, mobile numbers, residential addresses and loan-related identifiers can potentially be used to make fraudulent calls or messages appear credible.
For instance, a fraudster possessing information about a customer's banking relationship could impersonate a bank representative and attempt to obtain passwords, one-time passwords or other confidential credentials.
SBI advises customers not to disclose their internet banking passwords, ATM PINs, UPI PINs or OTPs to anyone, including callers claiming to represent the bank.
Customers should monitor account transactions, avoid opening suspicious banking links and verify unexpected communications through official bank channels.
Any unauthorised electronic banking transaction should be reported immediately. SBI provides a dedicated reporting number, 1800 1111 09, while suspected online financial fraud can also be reported through the national cybercrime helpline, 1930, or the government's cybercrime reporting portal.
Under the Reserve Bank of India's customer protection framework, liability for unauthorised electronic banking transactions depends on the circumstances and how promptly customers notify their bank.
The current incident has not established that any exposed record has been used to carry out financial fraud.
As the independent investigation continues, important questions remain unresolved, including the original source of the information, whether additional personal records are involved and what specific protective measures may be required for affected customers.
Delhi Police may seek further custody of CJP leaders Saurav Das, Ashutosh Ranka
SBI probes data leak after personal details in 3,897 customer records surface on dark web
Chennai Government Schools Face Drug Abuse Concerns as Teachers Call for Stronger Action
FUEL to Celebrate 20th Foundation Day and 2nd Convocation in Pune on October 24
Former Russian Test Cosmonaut Nikolai Tikhonov Discusses Space Exploration at Chennai Science Festival
Delhi Police may seek further custody of CJP leaders Saurav Das, Ashutosh Ranka
SBI probes data leak after personal details in 3,897 customer records surface on dark web
Sharjah schools set boundaries for AI use in homework and exams
Former MIT scientist wins $6 million defamation verdict in misconduct dispute
McMahon highlights Trump’s push to return education powers to states
Delhi Police may seek further custody of CJP leaders Saurav Das, Ashutosh Ranka
SBI probes data leak after personal details in 3,897 customer records surface on dark web
Chennai Government Schools Face Drug Abuse Concerns as Teachers Call for Stronger Action
FUEL to Celebrate 20th Foundation Day and 2nd Convocation in Pune on October 24
Former Russian Test Cosmonaut Nikolai Tikhonov Discusses Space Exploration at Chennai Science Festival
Delhi Police may seek further custody of CJP leaders Saurav Das, Ashutosh Ranka
SBI probes data leak after personal details in 3,897 customer records surface on dark web
Sharjah schools set boundaries for AI use in homework and exams
Former MIT scientist wins $6 million defamation verdict in misconduct dispute
McMahon highlights Trump’s push to return education powers to states
Copyright© educationpost.in 2026 All Rights Reserved.